-
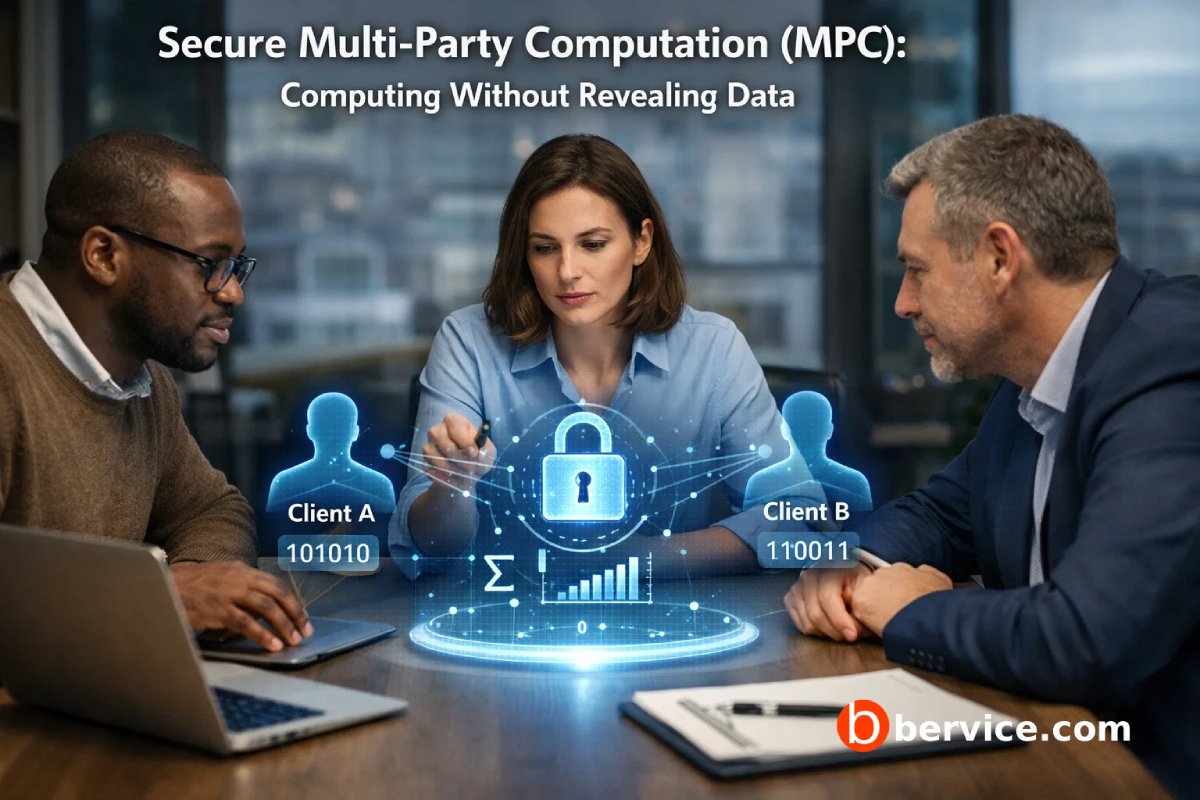
Secure Multi-Party Computation (MPC): Computing Without Revealing Data
In the digital economy, data collaboration is inevitable and dangerous. Governments, hospitals, banks, and platforms all need to compute over shared data, yet none of them can afford to expose raw inputs. Traditional security models force an impossible trade-off: either share the data or give up the computation. Secure Multi-Party Computation (MPC) exists precisely…
-
Secure Avionics Update & Patch Management
Why Software Updates in Aircraft Demand Zero-Tolerance Security Modern aircraft are no longer static machines; they are flying distributed systems. Flight control computers, navigation units, communication systems, and health-monitoring modules all depend on software that must evolve over time. But unlike consumer or enterprise systems, avionics software updates are safety-critical. A flawed update pipeline…
-
Hardware Hacking Attacks That Start at the Silicon Level
For years, cybersecurity has been dominated by a software-centric mindset. Firewalls, antivirus engines, EDR, and application security reviews all assume one thing: that the hardware beneath them is trustworthy. That assumption is increasingly wrong. Modern attackers do not stop at operating systems or applications they go deeper, down to firmware, microcode, and even the…
-
IPSec The Hidden Security Layer of the Internet
Before IPSec, the internet operated like an open street with no surveillance every packet was visible, traceable, and easy to manipulate. Data moved fast, but it moved naked. Anyone sitting in the right place on the network path could observe, replay, or tamper with traffic. IPSec was created to fix this fundamental flaw at…
-
Hidden Protocols in Networks: Beyond TCP/IP
Modern network security is still heavily shaped by assumptions made decades ago: traffic flows over well-known ports, protocols are explicit, and malicious behavior is noisy. Advanced attackers exploit exactly these assumptions. By using hidden or lesser-known protocol techniques, they turn the network into a gray zone where traditional visibility breaks down. The Illusion of…