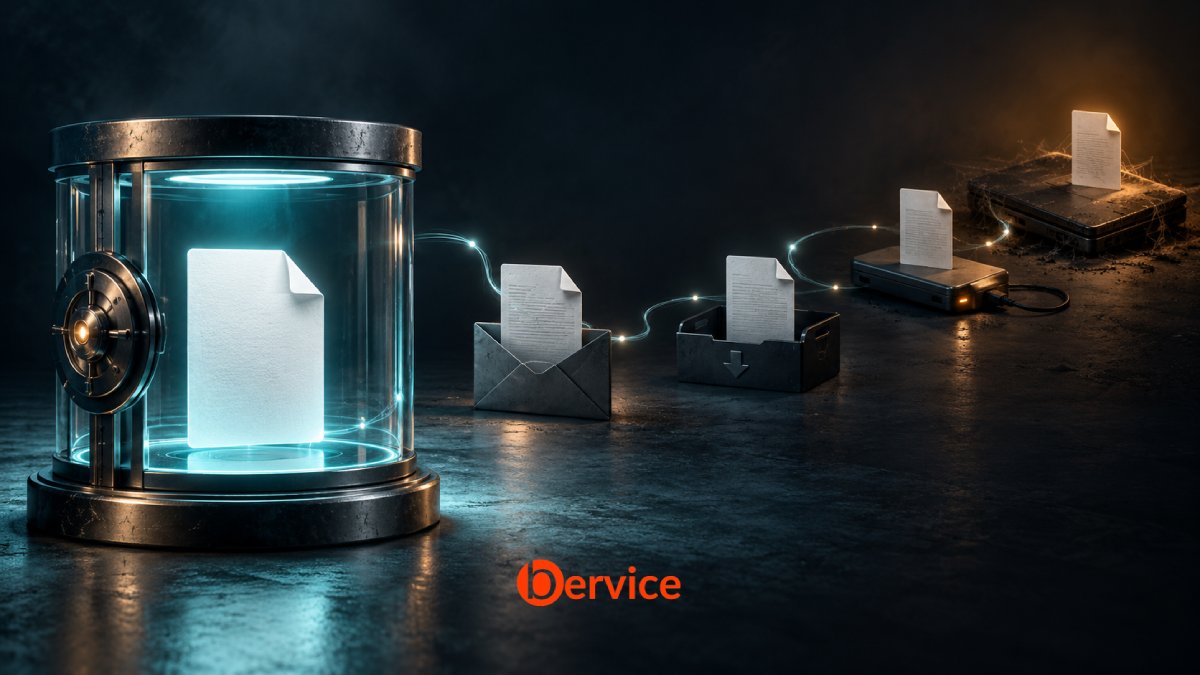
Your sensitive files may be protected where you keep them. What about everywhere they used to be?
You move an important document into a secure vault.
You check the password, review the access settings, and remove the original from your desktop. Everything appears to be in order.
But three months earlier, you emailed that document to yourself.
Two weeks later, you downloaded it onto another laptop.
Before moving it into the vault, you placed a copy in a folder called “Temporary.”
An old backup may still contain it. So might the computer you stopped using last year.
The document you are thinking about is protected. The copies you have forgotten may tell a different story.
This is one of the quieter problems in digital security: protecting information becomes harder when we no longer know where it exists.
How One File Becomes Many
Consider a hypothetical founder preparing documents for a business application.
They scan a passport with a phone, send the image to their email, download it onto a laptop, and attach it to an application. Later, they save a copy in company storage so they can find it again.
Each step serves a reasonable purpose. Together, those steps create several places to manage.
Depending on the applications and settings involved, there may also be a copy in the phone’s photo backup, an email attachment stored locally, a previous version in cloud storage, or a laptop backup.
None of this requires a security breach. Ordinary work creates duplication.
The problem emerges later, when the founder replaces the laptop, changes email providers, or decides the document is no longer needed. Removing the version they remember does not necessarily address the others.
A file can leave your attention long before it leaves your devices.
The Protection of One Copy Does Not Extend to Every Copy
We often describe information as though it has a single location:
“The contract is in our secure folder.”
“The identification documents are in the vault.”
“The financial records are encrypted.”
Those statements may accurately describe the versions currently in use. They say less about earlier downloads, attachments, exports, or backups.
Every independently accessible copy needs its own protection.
A carefully controlled document in one system does not automatically protect a previously downloaded version on another device. Encrypting a file today does not retroactively encrypt an older plaintext attachment.
This creates an important gap between where we intend sensitive information to live and where it actually remains.
An attacker does not need to access the copy with the strongest controls if another useful version is available elsewhere.
Forgotten Copies Lose Their Context
A temporary copy usually starts with a clear explanation:
“I need this for the meeting.”
“I will upload it later.”
“This is just for the application.”
Over time, the explanation disappears while the file remains.
A spreadsheet called export_final_2.csv may contain customer information. A ZIP archive may hold an entire project. A screenshot may include account details that nobody notices in the thumbnail.
Without context, people cannot easily determine whether a file is sensitive, whether it is still needed, or who is responsible for it.
Keeping it feels safer than deleting something potentially important. So it stays.
This is how temporary storage becomes a permanent archive without anyone deciding to create one.
Where Forgotten Copies Accumulate
Downloads folders
Downloads folders mix routine files with sensitive exports, signed agreements, identity documents, and financial statements.
Because downloading is usually a step toward another task, the downloaded copy can become invisible as soon as that task is complete.
The user remembers uploading the document. They may not remember leaving it behind.
Email attachments
Email is convenient for moving files between people and devices. It can also become an informal document archive.
An attachment may remain in sent mail, the recipient’s mailbox, a downloaded folder, or a backup. Deleting one message does not establish that every independently saved copy has disappeared.
Backups and version history
Recovery systems deliberately preserve earlier information.
A file removed from active storage may remain recoverable for a period determined by the backup or versioning system. That is useful when deletion was accidental, but it also means active storage and retained history need different handling.
Old devices and removable drives
A retired laptop, unused phone, or external drive can preserve a snapshot of a person’s digital life.
Being switched off reduces some forms of exposure. It does not establish that the stored information is protected against someone who later obtains access to the device.
Exports and working folders
Exports deserve particular attention because they can gather many records into one portable file.
A temporary spreadsheet created for analysis may contain more information than the person needed for the task. Once exported, it may sit outside the access controls and retention practices of the original system.
Backups Need Management, Not Elimination
There is a dangerous misunderstanding to avoid: fewer copies are not always safer.
A single copy can leave important information vulnerable to device failure, accidental deletion, or ransomware. Deliberate redundancy supports recovery.
CISA recommends maintaining offline, encrypted backups and regularly testing them. The objective is recoverable information with appropriate protection.
The useful distinction is between a managed backup and an abandoned duplicate.
A managed backup has a purpose, an owner, protection, and a retention process. Someone understands how it is restored and when older data expires.
An abandoned duplicate has no clear role. It survives because nobody has reviewed it.
The goal is to make necessary copies accountable.
Deleting a File Is a Location-Specific Action
“Deleted” sounds final, but its meaning depends on the system.
It may mean a file has moved to a recycle bin, disappeared from a shared folder, or been removed from active storage while historical versions remain. A recipient may also have saved an independent copy before deletion occurred.
For that reason, a useful deletion question is:
Deleted from which location, with what remaining retention?
That question is more precise than assuming one delete action covers an entire history of duplication.
It also matters before irreversible cleanup. Removing old copies without checking their purpose can destroy records or the only usable recovery version. A sensible review establishes what must be retained before deciding what can go.
Copies Can Become Outdated Without Becoming Harmless
A forgotten file does not need to be current to remain sensitive.
An old identity document may still reveal personal details. An expired agreement may contain signatures, pricing, and confidential terms. A superseded customer export may still contain contact information.
At the same time, outdated copies can create operational mistakes.
Someone may follow an obsolete instruction, use an earlier bank account detail, or make a decision from an incomplete report.
File duplication therefore creates two related problems:
- Confidentiality: information remains accessible where it is no longer needed.
- Integrity: people may rely on a version that is no longer authoritative.
Knowing which version is current helps with both, but marking a document “superseded” does not remove the sensitivity of its contents.
A More Practical Way to Regain Control
Perfect visibility across every historical copy may be unrealistic, particularly after files have been shared externally. Useful control can still improve substantially.
Start with the information that matters most
Trying to catalogue every file at once can turn a manageable review into an unfinished project.
Begin with categories whose exposure would have meaningful consequences: identity documents, financial records, customer exports, confidential agreements, and account recovery information.
For each category, ask where it normally enters the workflow, where people download or share it, and where it is retained.
Establish an authoritative home
People need a clear answer to “Where should I get the current version?”
An authoritative location reduces uncertainty and unnecessary duplication. Its value depends on people being able to find and use it easily.
If the approved location is difficult to access, people have a practical reason to create alternatives.
Give temporary copies an end point
“Temporary” should describe a duration or event.
A working copy might be needed until an upload is verified, a review is finished, or a project reaches an agreed milestone. The appropriate end point depends on the information and the workflow.
Making that end point explicit gives cleanup a reason to happen.
Review sharing methods
Where appropriate, controlled links can reduce attachment duplication and make future access easier to manage.
Their limits should remain clear. A link does not guarantee that a recipient cannot download, photograph, or otherwise reproduce accessible information. The benefit depends on the service, its settings, and the recipient’s actions.
Include backups and retired devices
A review that covers only active folders leaves out important parts of the information lifecycle.
Backup retention, restore procedures, old devices, and removable storage all belong in the conversation. Any disposal or erasure process should fit the actual device and storage technology, with necessary records and recovery needs checked first.
Restoring Data Can Restore Old Problems
Recovery deserves special attention because it can reintroduce information that was previously removed from active use.
Imagine restoring an old project backup after a device failure. Along with the needed work, the restore may bring back obsolete exports, superseded documents, or files whose retention period has ended.
A successful restore proves that information is recoverable. It does not, by itself, establish that everything restored should return to everyday use.
Recovery procedures should account for that distinction, especially when restoring older collections of sensitive information.
What This Means for Secure Vaults
A secure vault has a valuable role, but the surrounding workflow matters too.
If a person must repeatedly export sensitive files into ordinary folders to complete routine tasks, those working copies become part of the security picture.
Useful questions for evaluating a vault include:
- How does information enter and leave it?
- What happens when a user opens, downloads, or shares a file?
- Which protections continue after export?
- How are backups and recovery handled?
- What can the system actually confirm about deletion?
These questions help establish the boundary of protection.
For Bervice, the topic points to a clear principle: conversations about secure storage should include the lifecycle of the information being stored. A vault can protect the copies under its control. Claims about copies elsewhere require separate evidence.
Clear boundaries make security easier to understand and use responsibly.
Remembering Is Part of Control
Forgotten copies rarely begin with careless intentions.
They begin with a deadline, an upload, a meeting, or a useful backup. Each action makes sense at the time. The accumulated copies become difficult to manage because their original purpose fades.
A stronger approach gives sensitive information a known home, limits unnecessary duplication, protects recovery copies, and defines when temporary versions are no longer needed.
You may not be able to account for every copy ever created. You can make fewer copies disappear from your awareness.
The most dangerous copy may be the one you forgot exists, because it is the one you are no longer making decisions about.
Connect with us : https://linktr.ee/bervice
Website : https://bervice.com