Artificial intelligence is rapidly moving beyond chat interfaces. It is beginning to operate software, monitor equipment, process documents, manage workflows, and make thousands of small decisions across organizations.
But as AI becomes more operational, a difficult question appears: how can a business automate more without losing visibility and control?
One promising answer is a layered architecture built around two different types of intelligence:
- Small or specialized AI models running locally, close to the systems where work happens.
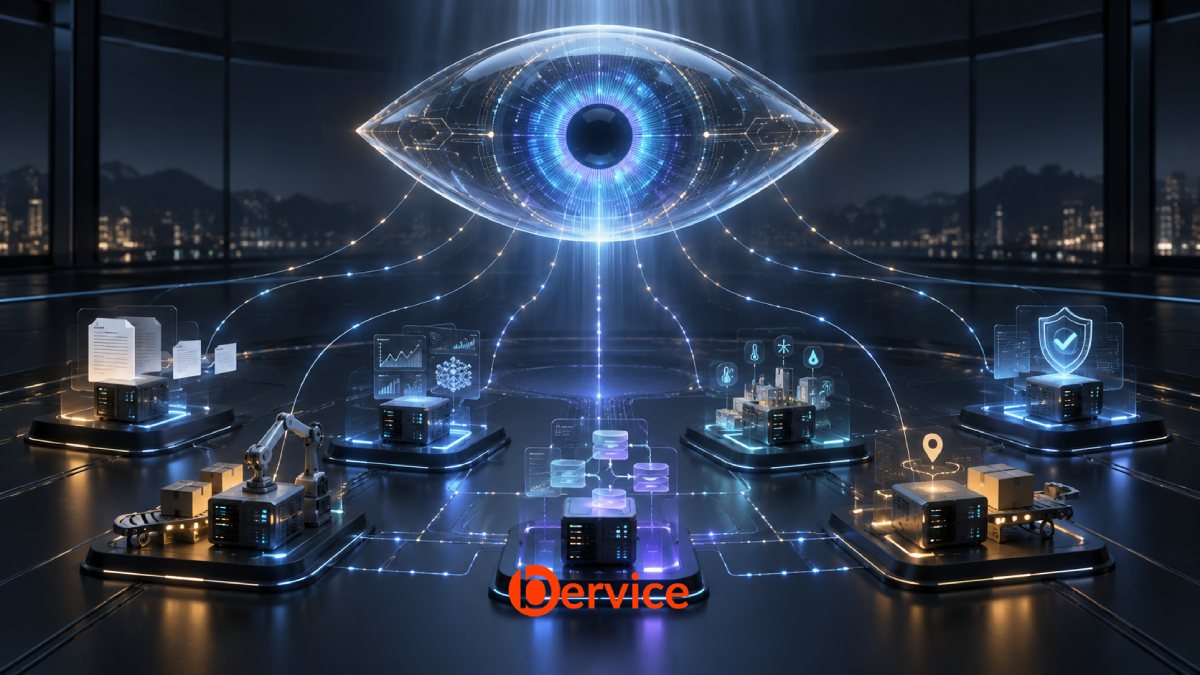
- A larger supervisory AI model positioned above them, observing their actions, evaluating risk, and intervening when necessary.
Think of the local models as skilled workers distributed throughout an organization. Each one understands a limited environment and performs a defined set of tasks. Above them sits a larger “supervisory eye” that does not need to execute every action itself. Its role is to see the wider picture, detect abnormal behavior, enforce policy, and decide when a human must become involved.
This model could become one of the most practical foundations for enterprise AI automation.
Why Local AI Models Matter
Most conversations about AI focus on very large cloud-based models. These models are powerful, general-purpose, and capable of handling complex reasoning. However, sending every operational task to a large remote model is not always efficient, affordable, private, or reliable.
Local AI changes the equation.
A local model can run on an employee’s computer, a company server, an industrial gateway, a vehicle, a camera system, or another edge device. It can work with information inside a controlled environment and respond without continuously transferring sensitive data to an external service.
For automation, this creates several important advantages.
Faster decisions
When a model runs close to the application or device, it can reduce network delays. This is especially useful for real-time monitoring, manufacturing, robotics, security systems, and operational alerts.
Greater privacy
Sensitive documents, images, recordings, customer data, and internal communications can remain inside the organization’s infrastructure. Only selected events, summaries, or risk signals need to be sent to the supervisory layer.
Lower operating costs
Routine decisions do not always require the largest available model. A smaller model trained or configured for a narrow task can often perform repetitive work at a much lower cost.
Continued operation during connectivity problems
A local automation system may continue performing approved tasks even when internet access is slow or temporarily unavailable. Its permissions can automatically become more restrictive while it is disconnected from central supervision.
Deeper specialization
A local model can be designed for one environment: checking invoices, classifying maintenance reports, detecting safety equipment, organizing files, monitoring a production line, or validating a specific business process.
The goal is not to make every local model universally intelligent. The goal is to make each model competent, predictable, and useful within a clearly defined boundary.
From One Powerful AI to a Network of Specialized Agents
Traditional software automation follows fixed rules. If a specific event occurs, the system performs a predefined action. AI automation is different because the system can interpret incomplete information, adapt to variation, and select among possible actions.
This flexibility is valuable, but it also introduces uncertainty.
A local AI agent may misunderstand a document. A camera model may misclassify an event. An email assistant may select the wrong recipient. A maintenance agent may recommend an action based on incomplete sensor data. Even a highly accurate model will eventually encounter unfamiliar conditions.
For this reason, local models should not be treated as independent digital employees with unlimited authority. They should operate as members of a controlled network.
Each agent should have:
- A defined purpose
- A limited set of tools
- Explicit data access boundaries
- A maximum level of authority
- Clear escalation conditions
- A complete activity record
- A method for stopping or reversing actions when possible
This is the first principle of safe automation: intelligence can be distributed, but authority must remain bounded.
The Supervisory Eye
Above the local agents sits a larger model with broader context. This is the supervisory eye.
It may run in a private cloud, a secure data center, or a carefully governed external AI service. Unlike local agents, it does not need to inspect every raw file or execute every small action. Instead, it receives structured information about what the agents are doing.
That information may include:
- The task an agent received
- The data sources it used
- Its proposed or completed action
- Its confidence level
- The permissions it requested
- Policy checks and validation results
- Unusual events or deviations
- The outcome of the action
The supervisory model compares this activity with company policies, historical patterns, risk thresholds, and the behavior of other agents. It can then approve, question, restrict, pause, or escalate an action.
The value of the supervisory eye comes from context. A local purchasing agent may see that an order is valid. The supervisor may see that similar orders were placed by three other agents within ten minutes, pushing the total above the approved budget. A local security model may consider a login normal. The supervisor may recognize that it conflicts with activity from another location.
The local agent understands the task. The supervisory model understands the system.
How the Architecture Works
A controlled AI automation cycle can be divided into six stages.
1. Observe
Local models monitor approved inputs such as files, sensors, application events, support requests, or workflow queues. Data collection should be limited to what the task genuinely requires.
2. Interpret
The local model classifies the event, extracts relevant information, and determines whether action is needed. It should generate a confidence score and identify uncertainty rather than hiding it.
3. Propose
Before using a tool, the agent creates a structured action proposal. The proposal explains what it wants to do, why it believes the action is appropriate, which resources will be affected, and whether the action can be reversed.
4. Evaluate
A policy engine performs deterministic checks. The supervisory model then evaluates contextual risk when necessary. Routine, low-risk actions may be automatically approved. Unusual or high-impact actions receive deeper review.
5. Execute
The local agent performs the approved action using narrowly scoped credentials. Permissions should be temporary whenever possible and limited to the exact tool and resource required.
6. Verify and learn
The system checks whether the intended result occurred. The outcome is recorded, and meaningful failures are used to improve prompts, policies, models, or approval thresholds. Learning must be governed. A production agent should not silently rewrite its own rules simply because an action appeared successful.
A Risk-Based Control Model
Not every action deserves the same level of oversight. Asking a human to approve every automation would remove much of the benefit. Allowing every agent to act freely would create unacceptable risk.
A better approach is to classify actions by impact.
Level 1: Observe only
The agent can read approved data and generate summaries or alerts, but it cannot change anything.
Level 2: Reversible internal actions
The agent can label a document, create a draft, organize a queue, or update a noncritical field. Every change is logged and can be reversed.
Level 3: Controlled operational actions
The agent can trigger an approved workflow, contact a known internal recipient, or adjust a system within a limited range. The supervisory layer checks context and policy before execution.
Level 4: High-impact actions
Payments, account deletion, legal commitments, production shutdowns, external publication, security changes, and decisions affecting employment or customer rights require explicit human authorization.
This structure allows autonomy to grow gradually. An agent can earn broader operational scope through evidence of reliable performance, but high-risk authority should never be granted solely because a model has been accurate in the past.
The Supervisor Must Also Be Controlled
Placing a larger model above local agents does not eliminate risk. It concentrates some risk at a higher level.
The supervisory model can misunderstand events, approve unsafe behavior, or become a single point of failure. If it has access to every raw dataset and every execution tool, a compromise could affect the entire organization.
The supervisory eye must therefore be governed by systems outside the model itself.
Critical controls include:
- Deterministic policy rules that the model cannot override
- Cryptographically protected audit logs
- Separation between observation, approval, and execution
- Independent identity for every agent and service
- Short-lived, narrowly scoped credentials
- Rate limits and financial limits
- Automatic shutdown conditions
- Version control for models, prompts, tools, and policies
- Regular adversarial testing
- Human review for high-impact decisions
The supervisor should recommend and coordinate. It should not become an invisible digital executive with unrestricted control.
What the Supervisory Eye Should Monitor
Good oversight is not the same as collecting everything. Constantly transmitting raw employee data, private conversations, video, or customer information to a central model can create serious privacy and security problems.
The system should monitor risk signals, not people by default.
Useful signals include unusual tool usage, repeated failures, sudden changes in confidence, attempts to access restricted information, unexpected communication patterns, conflicting agent actions, and outcomes that differ from the stated objective.
Where possible, local agents should convert sensitive activity into structured events. For example, the supervisor may need to know that a policy violation was detected, but not receive the full confidential document. Privacy filters and data minimization should exist before information reaches the central model.
This makes oversight more focused and reduces the amount of sensitive information concentrated in one place.
A Practical Example
Imagine a construction company using several local AI systems.
One model reviews camera feeds for missing safety equipment. Another monitors machinery telemetry. A third processes invoices. A fourth organizes daily site reports. Each model operates locally and has access only to the information required for its task.
The supervisory eye receives structured events from all four systems.
If the safety model detects a missing helmet, it can issue a local alert immediately. If similar alerts occur repeatedly in the same area while machinery telemetry shows active equipment, the supervisor can classify the situation as higher risk and notify a site manager.
If the invoice agent identifies a normal supplier invoice within an approved range, it can prepare the record automatically. If the amount is unusual, the supplier details recently changed, or related invoices appear across several projects, the supervisor can block payment and request human review.
No single local model sees the entire situation. The supervisory layer creates intelligence from coordination.
The Role of Humans
Human oversight must be more than a button labeled “approve.”
People need enough information to understand what the AI observed, what it intends to do, what could go wrong, and what alternatives exist. An approval request that contains only a confidence score is not meaningful oversight.
A strong human control interface should show:
- The proposed action in plain language
- The evidence supporting it
- Missing or conflicting information
- The systems and people that may be affected
- The estimated impact
- Whether the action can be reversed
- The reason automation was paused
Humans should also be able to stop an individual agent, suspend a category of actions, reduce permissions, inspect the history, and return the system to a known safe state.
The purpose of human involvement is not to compete with machine speed. It is to apply judgment where accountability, values, ambiguity, or irreversible consequences matter.
Building Trust Through Evidence
AI automation will not earn trust through impressive demonstrations alone. It will earn trust by producing evidence.
Organizations should be able to answer:
- Which model made the decision?
- Which version was running?
- What information did it use?
- Which policies were applied?
- Who approved the action?
- What tool executed it?
- What changed as a result?
- Can the action be reversed?
This creates an operational chain of responsibility. It also changes how AI performance is measured. Accuracy remains important, but it is not enough. A dependable agent must also be predictable, traceable, secure, policy-compliant, and capable of recognizing when it should stop.
The Future Is Hierarchical, Not Monolithic
The future of enterprise AI is unlikely to be one enormous model controlling every process directly. A more resilient design is hierarchical.
Small models will perform specialized work near the source of data. Larger models will coordinate across systems and evaluate complex situations. Deterministic software will enforce hard boundaries. Humans will retain authority over decisions with serious legal, financial, safety, or social consequences.
In this architecture, the “big eye” is not a symbol of unrestricted surveillance. It is a layer of accountable oversight. It watches the behavior of machines, not the private lives of people. It identifies patterns that individual agents cannot see, but it remains constrained by policy, security controls, and human authority.
Conclusion
Local AI models can make automation faster, more private, more resilient, and more affordable. Yet distributing intelligence across devices and workflows also distributes risk.
The answer is not to centralize every task in one powerful model. It is to build a system in which local agents can act within clear boundaries while a broader supervisory intelligence monitors context, coordinates behavior, and escalates uncertainty.
The strongest AI automation systems will not be the ones with the most autonomous agents. They will be the ones that know exactly where autonomy should end.
When local intelligence, central supervision, deterministic safeguards, and human accountability work together, automation becomes more than efficient. It becomes governable.
Connect with us : https://linktr.ee/bervice
Website : https://bervice.com